

Network Security Services
Network Security Services | Firewall Management, Network Protection, Threat Monitoring
Secure your network infrastructure with comprehensive security services designed to strengthen firewall controls, protect connected systems, and identify potential threats.
Get Started with Network Security
We only use your info to contact you about your IT needs.
Why Companies Choose AppStudio for Network Security Services
24/7 Reliability
24/7 monitoring of firewall health and security events means threats and outages are handled before they become breaches or downtime.
Stronger Security
Policy is designed, reviewed, and enforced consistently so remote workers and branch offices do not become the weak link.
Predictable Costs
One managed model replaces emergency break-fix work and overlapping security appliances with clear ownership.
Scalable Partnership
Architecture scales from a single office to multi-site and hybrid cloud without rewriting policy from scratch each time.
Services
What Our Network Security Services Cover
Firewall Policy Management
- Firewall rules designed, documented, and enforced across sites and remote access paths.
- Regular policy reviews that remove dead rules and reduce attack surface.
- Change control so urgent opens do not become permanent exceptions.
VPN & Site-to-Site Connectivity
- Secure remote VPN for hybrid and traveling staff.
- Site-to-site tunnels between offices, colo, and cloud networks.
- Access patterns that favor least privilege over flat network trust.
Zero-Trust Access
- Identity-aware access that verifies user and device before granting entry.
- Conditional access and MFA coordinated with your identity provider.
- Reduced reliance on broad VPN for every application.
Intrusion Prevention & Traffic Filtering
- IPS, web filtering, and traffic inspection tuned to your risk profile.
- Live threat intelligence applied to block known-bad destinations.
- Alert triage that separates noise from incidents that need action.
Network Segmentation
- Segmentation that keeps critical systems and sensitive data walled off.
- Guest, IoT, and corporate traffic separated with clear policy.
- Designs that limit blast radius when a device is compromised.
Firewall Health & Lifecycle
- Firmware, certificates, and high-availability monitored continuously.
- Capacity and performance reviews before bottlenecks hit users.
- Refresh planning so aging appliances are replaced on purpose, not in crisis.
Logging, Detection & Response
- Centralized logging with retention suited to your compliance needs.
- Coordination with SOC and cybersecurity services for escalation.
- Documented response playbooks for common network security incidents.
Compliance-Ready Network Controls
- Evidence of policy, change, and access reviews for auditors.
- Controls mapped to frameworks such as PCI DSS, HIPAA, and SOC 2.
- Alignment with your broader IT compliance and risk program.
Solving the Network Security Challenges that Others Overlook
Business Priorities
Industry Gaps
Our Proven Advantage
Global Standards. Built-In Trust.
We operate with the highest levels of security, privacy, and quality, backed by globally recognized certifications. Our standards are built to meet enterprise and regulatory requirements across industries.
Book a Free Consultation
Pick a time that works for you and walk through your current setup with one of our specialists. You will leave with a clear read on your options and a practical next step, with no obligation.
Rated Among the Top Managed IT Partners
Independent review platforms and analysts consistently rank AppStudio for the things clients care about most: reliability you can plan around, governance you can prove, and operations that scale as you do.


How We Onboard and Run Your Firewall & Network Security
Firewalls only protect what policy and monitoring keep honest. At AppStudio, we take over network security in phases so you get visibility first, then tighten segmentation and zero-trust access without breaking the business.
We operate with ITIL change practice and close coordination to your identity, endpoint, and SOC programs, including full IT managed services when you want one owner.
The outcome is a network perimeter and access model that auditors can follow and attackers find harder to traverse.
Why Clients Stay With Us
We are measured on blocked risk and uptime together. The numbers below are why clients keep network security with us.
Book a Free Consultation →average reduction in unused or duplicate firewall rules after the first policy cleanup
firewall high-availability uptime maintained across the production estates we operate
of network security clients renew after the first year
What Our Clients Say About Working With Us
Success Stories
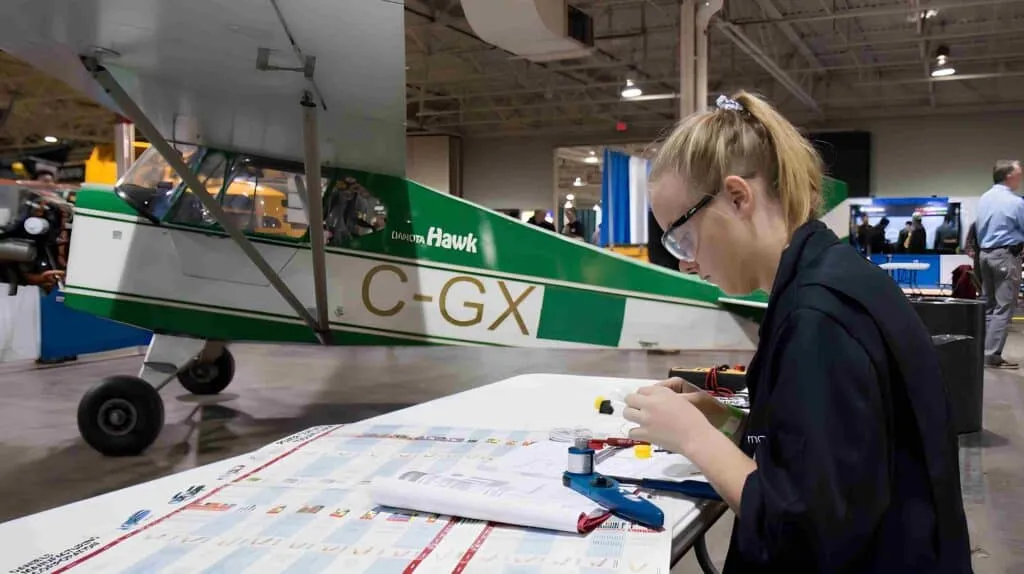
Empowering Future Talent in Trades and Technology
Commissioned by Skills Compétences Canada, we built a national bilingual platform with native apps, a secure CMS, and Canadian cloud infrastructure to promote trades and technology careers at scale.
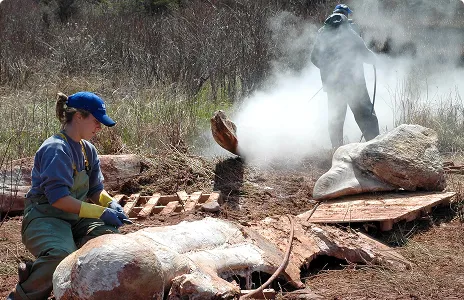
Digitizing Wildlife Surveillance for National Resilience
For the Canadian Wildlife Health Cooperative, we replaced siloed tools with a cloud-native platform that unifies field reports, lab diagnostics, and cross-province analytics in real time.
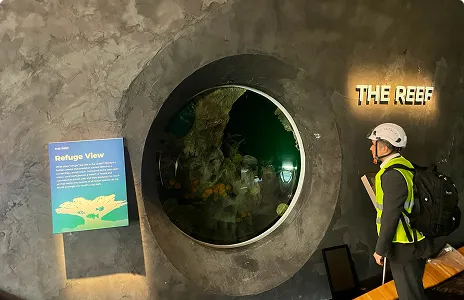
Interactive Learning Through Digital Experience
We unified kiosks, ticketing, and mobile into one cloud-native platform for Seattle Aquarium, raising visitor engagement and streamlining operations across every touchpoint.
Domain-Centric Network Security for Industry-Specific Needs
AppStudio manages firewalls and network security for industries that need segmented data, remote access, and audit-ready evidence without slowing operations.

Healthcare & Life Sciences
Healthcare & Life Sciences
- Segmented clinical, IoMT, and guest networks under least privilege.
- Zero-trust remote access for clinicians and third-party vendors.
- Firewalls and IPS tuned to shield EHR traffic and PHI.

Accounting & Financial Services
Accounting & Financial Services
- Zones isolating trading, payment, and back-office systems.
- DDoS and intrusion protection in front of client services.
- Encrypted, monitored links between branches and data centres.

Retail & Consumer Commerce
Retail & Consumer Commerce
- PCI-scoped segmentation walling off POS and payment paths.
- Store-to-cloud SD-WAN with firewalling and content filtering.
- Rogue-device and wireless intrusion detection in every store.

Government & Public Sector
Government & Public Sector
- Zone-based firewalls aligned to NIST and CIS baselines.
- Multi-agency networks with inspected east-west traffic.
- Least-privilege remote access with fully logged sessions.

Logistics, Supply Chain & Transportation
Logistics, Supply Chain & Transportation
- Warehouse, OT, and corporate traffic separated at the edge.
- Firewalled links for depots, docks, and mobile fleets.
- Intrusion detection spanning distributed, high-churn sites.

Telecom & Connectivity
Telecom & Connectivity
- Carrier-scale DDoS scrubbing at the network edge.
- Separation between core, subscriber, and management planes.
- Continuous inspection across very high-volume links.

Education & eLearning
Education & eLearning
- Student, staff, research, and IoT traffic kept apart.
- Campus-wide content filtering and safe-access controls.
- Policy-enforced remote and eduroam connectivity.

Travel, Hospitality & Aviation
Travel, Hospitality & Aviation
- Guest, POS, and operations traffic held firmly apart.
- Wireless intrusion detection across properties and terminals.
- PCI-scoped walls around booking and payment flows.

High-Tech, SaaS & Software Product Companies
High-Tech, SaaS & Software Product Companies
- Micro-segmentation and zero trust across cloud and pipelines.
- WAF, API, and egress controls in front of product traffic.
- East-west inspection between services and environments.

Real Estate & PropTech
Real Estate & PropTech
- Office, building-IoT, and access-control traffic separated.
- Hardened remote connectivity for agents and site teams.
- Firewalling for smart-building sensors and controllers.

Energy, Oil & Gas
Energy, Oil & Gas
- IT and OT segmentation drawn to IEC 62443 zones.
- Hardened remote paths into field and plant control systems.
- Intrusion detection across pipeline and terminal networks.

Manufacturing & Industrial
Manufacturing & Industrial
- Purdue-model layers between IT, OT, and SCADA.
- Deny-by-default firewalling around cells and production lines.
- OT-aware intrusion detection on the plant floor.

Media & Entertainment
Media & Entertainment
- Production, edit, and distribution traffic partitioned.
- DDoS protection for streaming and high-traffic platforms.
- Monitored, least-privilege access to high-value content.

Legal Services & Law Firms
Legal Services & Law Firms
- Tight segmentation and least privilege around case systems.
- Encrypted, monitored remote access for lawyers and staff.
- Firewalls and IPS guarding privileged matter data.

Nonprofit Organizations
Nonprofit Organizations
- Right-sized firewalling and segmentation for lean networks.
- Simple, hardened remote and volunteer access.
- Budget-fit content filtering and intrusion alerts.

Pharmaceuticals & MedTech
Pharmaceuticals & MedTech
- Lab, manufacturing, and validated-system traffic separated.
- Firewalls and access control ringing GxP environments.
- Intrusion detection shielding research and trial data.
A Firewall Estate That Is Governed, Not Just Installed
A firewall full of exceptions is not a control. It is a history of emergencies. Managed network security replaces that drift with policy, monitoring, and ownership.
We manage firewalls, VPN, zero-trust access, IPS, and segmentation as an operating service. For deeper detection and response, pair this with cybersecurity services or a broader IT managed services engagement.
If you want a partner who will own the rule base and the 2 a.m. tunnel alert, book a consultation.
Book a Free Consultation →
Frequently Asked Questions
Segment. Enforce. Monitor.
Stand up network security and firewall management that protects every site and remote worker with policy you can prove.
Book a Free Consultation →
Request a Consultation
Tell us a little about your setup using the form below and our service delivery team will reach out to talk through your environment, your priorities, and the approach that fits best.

