

Governance, Risk and Compliance
Governance, Risk and Compliance | Control Frameworks, Live Risk Registers, Audit-Ready Evidence
AppStudio runs governance, risk, and compliance as one program instead of three disconnected efforts. We align your controls to ISO 27001, SOC 2, and NIST, quantify and track risk in a live register, and keep documented, defensible evidence ready for every audit.
Tell Us About Your GRC Program
We only use your info to contact you about your IT needs.
Why Teams Trust AppStudio for GRC Management
Always Audit-Ready
Your GRC management runs on continuous control monitoring, so gaps are caught and closed early and findings do not surface for the first time during an audit.
Risk You Can See
Your IT risk and compliance posture is scored, ranked, and tracked in a live register, so leadership sees real exposure instead of guesswork.
Predictable Compliance
A structured governance risk and compliance framework replaces last-minute remediation with planned, budgeted compliance work you can forecast.
A Program That Scales
One control set covers many frameworks, so your IT GRC scales as you enter new markets and take on new obligations.
Services
What Our GRC Services Cover
Compliance & Framework Alignment
- Programs mapped to ISO 27001, SOC 2, NIST, HIPAA, PCI DSS, and GDPR.
- One control set that satisfies multiple frameworks without duplicated work.
- Control libraries tailored to your industry and obligations.
Enterprise & IT Risk Management
- Risk assessments that identify, score, and rank real exposure.
- A live risk register kept current as your environment changes.
- Prioritized treatment plans tied to business impact and risk appetite.
Governance & Policy Development
- Enforceable security and IT policies mapped to your frameworks.
- Governance structures that assign control owners and accountability.
- Policy lifecycle management with scheduled reviews and version control.
Audit Readiness & Support
- Readiness assessments that surface gaps before the auditor does.
- Evidence collected and mapped to each control requirement.
- Hands-on support through the audit, from kickoff to findings.
Continuous Control Monitoring
- Automated checks on key controls and configurations.
- Alerting on control drift so issues are fixed before they become findings.
- Dashboards that show compliance and risk posture in real time.
Data Privacy & Protection
- Data classification, access control, and encryption aligned to privacy law.
- Retention, disposal, and data-lifecycle governance.
- Support for data-subject rights and breach-notification duties.
Third-Party & Vendor Risk
- Vendor and partner assessments against your risk criteria.
- Due-diligence workflows across onboarding and renewal.
- Ongoing monitoring of third-party posture and contract obligations.
Security Awareness & Training
- Role-based training that turns staff into a first line of defense.
- Phishing simulations and measurable awareness programs.
- Completion records that double as audit evidence.
One GRC program that keeps governance, risk, and compliance in step all year round.
Get Your GRC Program Assessment ›We passed SOC 2 on the first try, and compliance stopped being a quarterly fire drill.CISO, SaaS
Solving the GRC Challenges that Others Overlook
Business Priorities
Industry Gaps
Our Proven Advantage
Global Standards. Built-In Trust.
We operate with the highest levels of security, privacy, and quality, backed by globally recognized certifications. Our standards are built to meet enterprise and regulatory requirements across industries.
Book a Free Consultation
Pick a time that works for you and walk through your current setup with one of our specialists. You will leave with a clear read on your options and a practical next step, with no obligation.
A Compliance and Risk Management Partner Teams Rely On
Independent review platforms rank AppStudio for what compliance and security leaders weigh most in governance and risk management: clean audits, risk that is visible and managed, and evidence that holds up to scrutiny.


The Platforms Behind Our GRC Program
The platforms behind our program span compliance automation, privacy, risk, and monitoring, chosen for evidence quality, coverage, and the real-time visibility that day-to-day GRC management runs on. Every tool below is one we operate and manage inside your environment.
 Vanta
 Drata
 AuditBoard
 Cynomi
 ServiceNow GRC
 OneTrust
 Okta
 Entra ID
 Microsoft Intune
 CrowdStrike Falcon
 SentinelOne
 Bitdefender GravityZone
 Sophos Central
 Splunk
 Datadog
 Elastic Stack
 ServiceNow CMDB
 Terraform
 Microsoft Defender
 Proofpoint
 Mimecast
How We Run Your IT Risk and Compliance Program
Compliance done once a year is compliance you cannot trust. What works is a living governance risk and compliance program that monitors controls, manages risk, and keeps evidence current. At AppStudio, we build it in clear phases so you reach a defensible baseline quickly and tighten it every quarter.
The program keeps governance risk management and compliance grounded in recognized frameworks, automation, and ownership, with each phase tied back to what leadership cares about: lower risk, clean audits, and controls you can prove on demand.
The result is an IT governance risk and compliance framework that runs in the background of the business, with the reporting to show exactly where you stand at any moment.
Why Compliance Teams Stay With Us
We are measured on clean audits and risk that is actually going down, not on activity. The numbers below are why clients keep their GRC program with us.
Scope Your Compliance Program →of clients we support cleared their audit the first time through
average cut in high-priority findings within the first year
of key controls under continuous monitoring across supported frameworks
What Our Clients Say About Working With Us
Success Stories
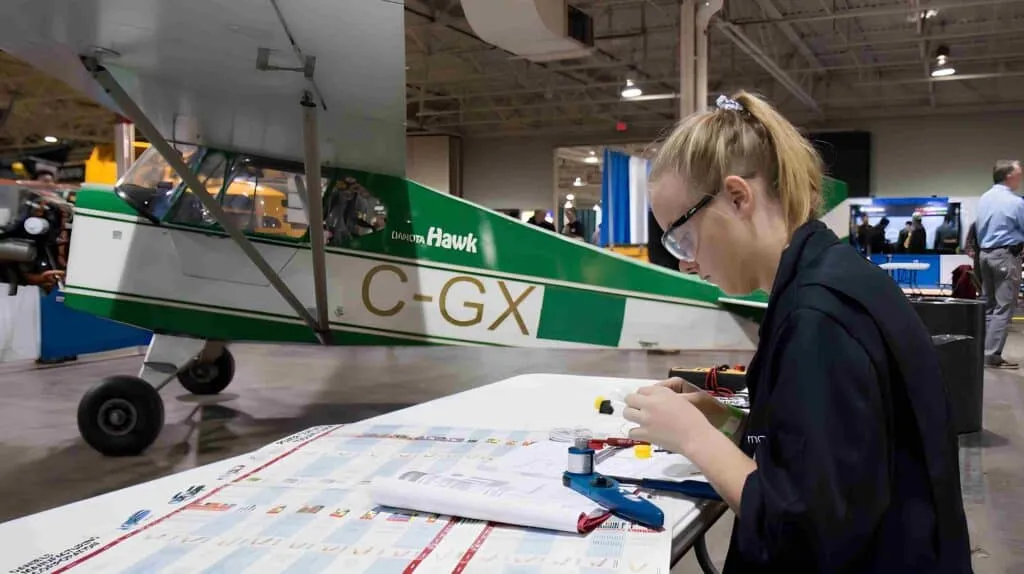
Empowering Future Talent in Trades and Technology
Commissioned by Skills Compétences Canada, we built a national bilingual platform with native apps, a secure CMS, and Canadian cloud infrastructure to promote trades and technology careers at scale.
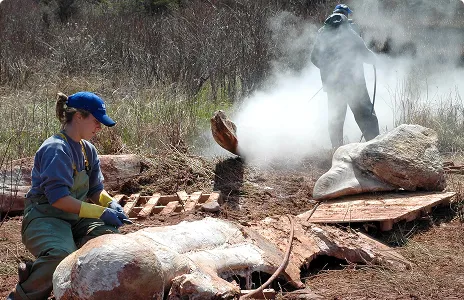
Digitizing Wildlife Surveillance for National Resilience
For the Canadian Wildlife Health Cooperative, we replaced siloed tools with a cloud-native platform that unifies field reports, lab diagnostics, and cross-province analytics in real time.
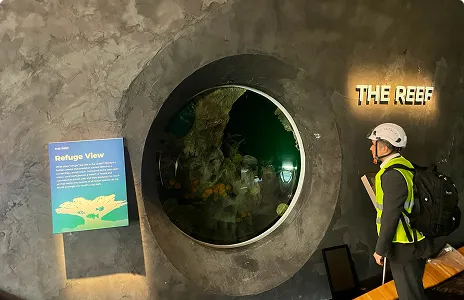
Interactive Learning Through Digital Experience
We unified kiosks, ticketing, and mobile into one cloud-native platform for Seattle Aquarium, raising visitor engagement and streamlining operations across every touchpoint.
Governance, Risk and Compliance for Every Industry We Serve
We tailor governance, risk, and compliance programs to the frameworks and obligations each sector carries, pairing standardized control libraries with domain expertise for clean audits and lower risk.

Healthcare & Life Sciences
Healthcare & Life Sciences
- HIPAA and PHIPA control programs with mapped safeguards for PHI across clinical systems.
- Risk registers that track exposure across EHR, connected devices, and third-party vendors.
- Audit-ready evidence and breach-response readiness for regulators and health-system partners.

Pharmaceuticals & MedTech
Pharmaceuticals & MedTech
- GxP and 21 CFR Part 11 controls with validated, monitored, audit-ready environments.
- Risk assessments across R&D, trials, and production backed by a maintained register.
- Data-integrity, retention, and evidence controls mapped to regulator expectations.

Retail & Consumer Commerce
Retail & Consumer Commerce
- PCI DSS scoping, segmentation, and evidence across stores, e-commerce, and payments.
- Vendor and third-party risk management for processors and platform partners.
- Continuous monitoring that keeps card-data controls audit-ready all year.

Government & Public Sector
Government & Public Sector
- Programs aligned to NIST and CIS with complete, defensible audit trails.
- IT governance risk and compliance with named control owners and clear accountability.
- Documented controls ready for oversight, funding reviews, and multi-agency work.

Logistics, Supply Chain & Transportation
Logistics, Supply Chain & Transportation
- Risk controls spanning WMS, TMS, EDI, and distributed depot and fleet systems.
- Third-party and supply-chain risk assessed, scored, and monitored continuously.
- Access controls and evidence that hold up across high-churn, distributed sites.

Telecom & Connectivity
Telecom & Connectivity
- Governance and risk management across OSS/BSS, network, and subscriber data.
- Controls mapped to SOC 2 and privacy duties for high-volume subscriber platforms.
- Continuous monitoring and audit evidence for always-on core infrastructure.

Education & eLearning
Education & eLearning
- FERPA- and privacy-aware controls protecting student and staff records.
- Access governance and risk registers across SIS, LMS, and campus systems.
- Evidence and controls ready for funding, accreditation, and privacy reviews.

Travel, Hospitality & Aviation
Travel, Hospitality & Aviation
- PCI DSS and privacy controls across booking, PMS, POS, and loyalty systems.
- Vendor governance and monitoring across properties, franchises, and locations.
- Continuous monitoring and evidence for service- and safety-critical operations.

High-Tech, SaaS & Software Product Companies
High-Tech, SaaS & Software Product Companies
- SOC 2 and ISO 27001 programs that turn security into a sales asset.
- Continuous control monitoring across cloud, CI/CD, and multi-tenant infrastructure.
- GRC services that keep controls and evidence current between audits as you ship.

Real Estate & PropTech
Real Estate & PropTech
- Controls and risk registers spanning offices, smart-building, and access systems.
- Vendor and data-protection governance for connected PropTech platforms.
- Records and evidence covering acquisitions, disposals, and tenant data duties.

Energy, Oil & Gas
Energy, Oil & Gas
- NERC CIP and IEC 62443 aligned governance across converged IT and OT.
- Risk scoring and monitoring for critical assets, field systems, and control networks.
- IT risk and compliance evidence kept current for regulators and auditors.

Manufacturing & Industrial
Manufacturing & Industrial
- IEC 62443 aligned controls spanning corporate IT and plant-floor OT systems.
- Risk assessments and segmentation protecting MES, SCADA, and ERP environments.
- Change control and evidence that keep production systems audit-ready.

Media & Entertainment
Media & Entertainment
- Content, IP, and rights-data protection with mapped access controls.
- Vendor governance and risk registers across production and distribution.
- Monitoring and evidence that protect rights, royalties, and master assets.

Legal Services & Law Firms
Legal Services & Law Firms
- Confidentiality and data-protection controls safeguarding client matter data.
- Matter-level access controls and risk tracking across document and case systems.
- Retention and evidence controls that satisfy regulators and clients.

Nonprofit Organizations
Nonprofit Organizations
- Right-sized compliance and risk management aligned to funder and donor duties.
- Access governance and data protection for donor and beneficiary records.
- Evidence and controls that stay audit-ready on a limited budget.

Accounting & Financial Services
Accounting & Financial Services
- Governance risk and compliance mapped to SOC 2, PCI DSS, and SOX.
- Scored, ranked financial and IT risk reported to leadership and examiners.
- Version-controlled policies and evidence that hold up to auditors and clients.
Trusted to Keep Governance, Risk and Compliance in One Program, All Year
Compliance should protect the business and earn trust, not consume your team every audit season. Organizations across North America rely on our governance, risk & compliance services to keep controls current, risk managed, and evidence audit-ready.
With framework-aligned programs, continuous monitoring, and disciplined governance, our GRC managed services turn compliance from a periodic scramble into a standing capability. We score risk, close gaps, and keep documentation defensible, all tied to your workflows and roadmap. Need broader coverage? Explore our full IT managed services or dedicated cybersecurity services.
If you want a partner that leads with rigor, accountability, and clean audits, book your strategy call below.
Book Your Governance and Risk Review →
Frequently Asked Questions
Govern. Manage Risk. Prove Compliance.
Stand up a governance, risk, and compliance program that lowers exposure and stays audit-ready, with the control ownership and evidence growing organizations need.
Start Your GRC Program →
Request a Consultation
Tell us a little about your setup using the form below and our service delivery team will reach out to talk through your environment, your priorities, and the approach that fits best.

