

Managed Security Service Provider
Fully Managed Security Services Provider | 24/7 Threat Monitoring, Rapid Incident Response, and Resilient Security
Our MSSP offerings provide continuous monitoring, threat detection, and rapid response to protect your business from cyber attacks. We deliver expert security management, enforce policies, and reduce risk while freeing your team to focus on core operations.
Fill the form to Secure Your Business with Managed Security
We only use your info to contact you about your security needs.
Why Security Leaders Choose AppStudio as Their MSSP
Proactive Threat Protection
Our managed security services watch your endpoints, identities, network, and cloud around the clock, hunt for threats before they detonate, and shut down attacks while they are still small.
Compliance Made Provable
As a managed cyber security services team, we map controls, evidence, and reporting to SOC 2, ISO 27001, HIPAA, and PCI DSS, so audits become a formality instead of a fire drill.
Expert Security, No Hiring
Unlike most managed security providers, we give you certified SOC analysts, threat hunters, and a virtual CISO without the cost, ramp time, or attrition risk of building an in-house team.
Scales With Your Risk
Add users, sites, clouds, and frameworks as you grow. Our IT managed security services flex with your environment on flat, predictable monthly pricing.
Services
End-to-End Managed Security Services
Managed Detection & Response (MDR / XDR)
- 24/7 monitoring with real-time alerting, triage, and analyst-led investigation.
- Telemetry correlated across endpoints, identities, network, and cloud in one view.
- Guided containment and remediation led by certified SOC responders.
SOC as a Service & SIEM
- Centralized log collection, normalization, and long-term retention.
- Detection engineering and correlation tuned to cut noise and surface real risk.
- Compliance and audit dashboards your leadership can actually read.
Endpoint Protection & EDR
- Behaviour-based detection with one-click isolation and rollback.
- Policy-driven hardening, disk encryption, and device control.
- Full coverage across Windows, macOS, Linux, and mobile fleets.
Identity & Access Security
- MFA and single sign-on rolled out and enforced across your stack.
- Least-privilege and role-based access with continuous review.
- Privileged access monitoring and identity threat detection.
Email & Collaboration Security
- Defense against phishing, spoofing, and business email compromise.
- Attachment sandboxing, URL rewriting, and impersonation protection.
- Encryption and policy-based filtering across Microsoft 365 and Google Workspace.
Network, Firewall & Zero Trust
- Centralized firewall and VPN policy enforced across sites and remote workers.
- Zero-trust segmentation with identity-aware access controls.
- Intrusion detection and continuous traffic inspection.
Cloud Security & CSPM
- Real-time detection of misconfigurations across AWS, Azure, and GCP.
- Compliance posture monitoring mapped to your frameworks.
- Shift-left guardrails integrated into your CI/CD pipelines.
Vulnerability & Penetration Testing
- Continuous vulnerability scanning with exploit validation and prioritization.
- Red-team and penetration testing that exposes real-world attack paths.
- Remediation tracking until risk is actually closed, not just reported.
Incident Response & Digital Forensics
- Rapid triage, containment, and root-cause analysis when it matters most.
- Memory, disk, and network forensics during active breach events.
- Post-incident reporting and hardening so the same gap never reopens.
Compliance & Governance (GRC)
- Framework alignment for SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS.
- Policy development, control mapping, and governance advisory.
- Audit preparation, evidence collection, and ongoing compliance tracking.
Data Protection & DLP
- Data classification, tagging, and access controls across endpoints and cloud.
- DLP policy enforcement that follows sensitive data wherever it moves.
- Monitoring and alerting on exfiltration and insider-risk activity.
Threat Intelligence & Security Advisory (vCISO)
- Dark-web monitoring for leaked credentials and brand impersonation.
- Third-party and supply-chain risk monitoring with actionable alerts.
- Virtual CISO leadership for roadmaps, board reporting, and security strategy.
One accountable managed security services provider across every layer of your attack surface.
Book My Free Consultation ›They contained an active intrusion in under 20 minutes and walked us through our SOC 2 audit without a single open finding.CISO, Financial Services
Solving the Security Challenges that Others Overlook
Business Priorities
Industry Gaps
Our Proven Advantage
Global Standards. Built-In Trust.
We operate with the highest levels of security, privacy, and quality, backed by globally recognized certifications. Our standards are built to meet enterprise and regulatory requirements across industries.
Book a Free Security Consultation
Pick a time that works for you and walk through your current security posture with one of our advisors. You will leave with a clear read on your biggest risks and a practical next step, with no obligation.
Recognized Among Leading Managed Security Services Providers
Independent review platforms and analysts consistently rank AppStudio for what security buyers care about most: fast detection and response, provable compliance, and a SOC that operates like an extension of your own team.


An Integrated Managed Cyber Security Stack for End-to-End Protection
We operate and integrate industry-leading security platforms across the SOC, endpoint, identity, cloud, and compliance layers, chosen for visibility, speed of response, and proven detection efficacy. Here is the tooling we run inside your environment.
 Splunk
 Elastic Security
 Graylog
 Logz.io
 CrowdStrike Falcon
 SentinelOne Singularity
 Microsoft Defender for Endpoint
 Bitdefender GravityZone
 Sophos Intercept X
 Huntress
 Proofpoint
 Mimecast
Microsoft Defender for Office 365
 Barracuda
 Okta
 Microsoft Entra ID
 Duo Security
 JumpCloud
 CyberArk
 Vanta
 Drata
 AuditBoard
 OneTrust
 Cynomi
 Keeper
 1Password
CyberArk
 Cisco Meraki
 SolarWinds
 Acronis Cyber Protect Cloud
 NinjaOne
How We Use the NIST Cybersecurity Framework to Protect You
Our managed security program is grounded in the NIST Cybersecurity Framework (CSF). Its five core functions, Identify, Protect, Detect, Respond, and Recover, give us a structured, repeatable way to reduce risk and keep your business resilient against evolving threats.
Identify
We start by understanding what we are protecting. We map your assets, users, data flows, third-party dependencies, and existing controls, then profile your real-world risk against the compliance frameworks you answer to, so nothing critical sits in a blind spot.
Protect
We harden your environment with layered, proactive controls, from identity and access management and endpoint hardening to email security, segmentation, and least-privilege enforcement, all calibrated to your operations rather than a generic template.
Detect
Our 24/7 SOC continuously monitors endpoints, identities, network, and cloud, correlating telemetry through tuned detection logic so genuine threats surface fast and alert fatigue stays low.
Respond
When something looks wrong, our analysts triage, contain, and investigate in real time using defined runbooks. High-severity activity is isolated immediately, and you are kept informed with clear action steps, never left guessing.
Recover
We restore normal operations quickly with tested backup, disaster recovery, and continuity plans, then run a post-incident review so the same weakness cannot be used against you twice.
How We Onboard and Run Your Managed Cyber Security Services
The more complex your environment becomes, the less a reactive, tool-only approach can keep up. What you need is a security operation that builds resilience, responds fast, and improves every month. At AppStudio, our delivery model is structured, outcome-oriented, and refined across hundreds of engagements.
We work in clear phases so onboarding is smooth, coverage is complete, and results are measurable. Roles, SLAs, escalation paths, and reporting cadence are defined upfront, which removes ambiguity and gives your leadership full visibility from day one.
By pairing deep security expertise with disciplined governance, our cyber security managed services move you from chasing alerts to a program that genuinely lowers risk, not just one that shifts the workload.
Proven by Results
Our clients stay with us because we deliver what matters
Talk to Our Security Advisors →Clients Say They Now Spend Less Time on Internal Security Operations
Clients Retained Over the Past 3 Years Without Contract Renegotiation
Clients Say We Helped Them Pass Their Compliance Audit
How We Deliver Value, in Our Clients’ Words
Success Stories
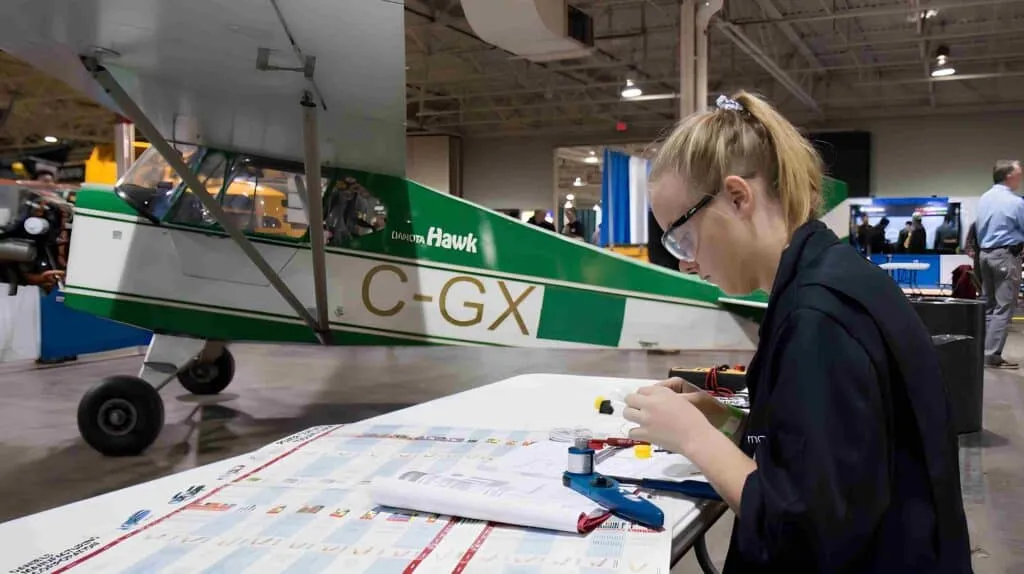
Empowering Future Talent in Trades and Technology
Commissioned by Skills Compétences Canada, we built a national bilingual platform with native apps, a secure CMS, and Canadian cloud infrastructure to promote trades and technology careers at scale.
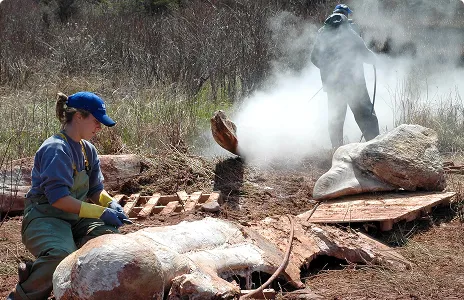
Digitizing Wildlife Surveillance for National Resilience
For the Canadian Wildlife Health Cooperative, we replaced siloed tools with a cloud-native platform that unifies field reports, lab diagnostics, and cross-province analytics in real time.
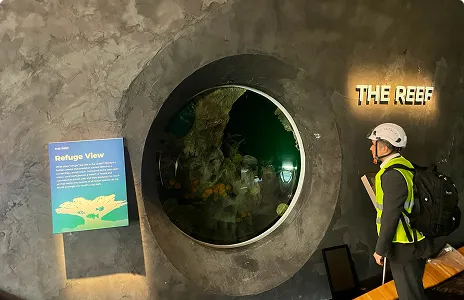
Interactive Learning Through Digital Experience
We unified kiosks, ticketing, and mobile into one cloud-native platform for Seattle Aquarium, raising visitor engagement and streamlining operations across every touchpoint.
Industries We Secure as a Managed Security Service Provider
As one of the more experienced managed IT security service providers, AppStudio delivers industry-specific MSSP services tuned to the operational realities, regulatory obligations, and threat landscape of each sector. We combine deep domain knowledge with standardized security governance to protect critical systems and data without slowing the business.

Healthcare & Life Sciences
Healthcare & Life Sciences
- 24/7 SOC with SIEM and XDR across EHR, medical devices, and clinical networks.
- Managed detection and threat hunting tuned to protect PHI and patient safety.
- HIPAA/PHIPA controls, incident response, and audit-ready evidence.

Accounting & Financial Services
Accounting & Financial Services
- Continuous threat detection and SOC monitoring across banking and trading systems.
- Fraud, insider-threat, and account-takeover analytics with rapid containment.
- SOC 2, PCI DSS, and financial-regulation controls with 24/7 response.

Retail & Consumer Commerce
Retail & Consumer Commerce
- PCI-DSS SOC monitoring across POS, e-commerce, and payment flows.
- Bot, fraud, and account-takeover defense that holds through peak demand.
- Managed detection and threat intelligence across stores, cloud, and apps.

Government & Public Sector
Government & Public Sector
- SOC and SIEM aligned to NIST 800-53, CIS, and public-sector mandates.
- Threat hunting and incident response across multi-agency estates.
- Continuous monitoring and audit trails protecting citizen data and services.

Logistics, Supply Chain & Transportation
Logistics, Supply Chain & Transportation
- Converged IT/OT threat detection across fleet, warehouse, and edge systems.
- Ransomware defense and digital forensics that keep operations moving.
- Third-party and supply-chain risk monitoring with threat intelligence.

Telecom & Connectivity
Telecom & Connectivity
- Carrier-scale SOC covering core network and subscriber platforms.
- DDoS, fraud, and intrusion detection with SLA-backed response.
- Threat hunting and SIEM correlation across high-volume traffic.

Education & eLearning
Education & eLearning
- FERPA-aware managed detection for student data, LMS, and campus networks.
- Phishing, ransomware, and account-compromise defense with rapid response.
- SOC-as-a-service scaled for lean IT teams and budgets.

Travel, Hospitality & Aviation
Travel, Hospitality & Aviation
- PCI-aligned SOC across booking, PMS, POS, and loyalty systems.
- 24/7 monitoring and managed detection across properties and guest networks.
- Incident response that safeguards guest data and keeps systems online.

High-Tech, SaaS & Software Product Companies
High-Tech, SaaS & Software Product Companies
- Cloud-native SOC and posture management for multi-tenant SaaS and CI/CD.
- DevSecOps, EDR/XDR, and continuous vulnerability management.
- SOC 2 / ISO 27001 evidence, threat hunting, and audit support built in.

Legal Services & Law Firms
Legal Services & Law Firms
- Confidentiality-first SOC monitoring for DMS and case systems.
- Email, ransomware, and data-exfiltration defense with forensics.
- Privileged-access protection and audit-ready security controls.

Media & Entertainment
Media & Entertainment
- SOC and content-security monitoring for pipelines, streaming, and IP.
- DDoS and account-abuse defense for high-traffic platforms.
- Managed detection and threat hunting across cloud, storage, and delivery.

Manufacturing & Industrial
Manufacturing & Industrial
- Converged IT/OT SOC across plants, SCADA, and ICS.
- Ransomware and intrusion defense that protects production uptime.
- Network segmentation, hardening, and IEC 62443-aligned controls.

Energy, Oil & Gas
Energy, Oil & Gas
- Round-the-clock SIEM and SOC spanning converged IT and OT estates.
- Critical-asset controls mapped to NERC CIP and IEC 62443 obligations.
- Co-managed response that respects plant safety and uptime limits.

Real Estate & PropTech
Real Estate & PropTech
- Managed SIEM over leasing portals, smart-building tech, and apps.
- Wire-fraud and phishing defense on closing and deposit workflows.
- One SOC view across head office, branches, and on-site crews.

Nonprofit Organizations
Nonprofit Organizations
- A full outsourced SOC sized for small teams and grant budgets.
- Ransomware and account-takeover defense across donor and grant systems.
- Governance and reporting that reassure funders and boards.

Pharmaceuticals & MedTech
Pharmaceuticals & MedTech
- Managed SIEM and threat hunting across R&D and production networks.
- Protection for trial data, formulas, and regulated plant systems.
- GxP-conscious monitoring with audit-ready incident records.
Your 24/7 Security Team: Stopping Threats and Keeping 100+ Organizations Audit-Ready
AppStudio is a trusted managed security service provider for startups, enterprises, and public-sector organizations, delivering end-to-end protection across endpoints, identities, cloud environments, and critical infrastructure. Our 24/7 threat detection, incident response, and compliance support keep your business secure while your team stays focused on growth.
Operating as a fully managed extension of your organization, our certified SOC analysts, threat hunters, and incident responders provide proactive coverage, measurable risk reduction, and high-availability protection, with the integrated telemetry and multi-tenant SOC capabilities that give you complete visibility without the complexity of managing it yourself.
Today we safeguard organizations across Canada and the US, delivering managed security services these businesses trust across highly regulated industries such as healthcare, finance, legal, and SaaS. Whether you need a full MSSP or a co-managed SOC to extend your team, we shape the engagement around your real risk. Explore our cybersecurity services or compare our managed IT services if you also need broader infrastructure support.
Book a Free Security Consultation →
Frequently Asked Questions
Detect. Respond. Stay Compliant.
Stand up a managed security program built for what is next, with the 24/7 coverage, provable compliance, and rapid response that modern organizations need from their MSSP.
Book a Free Security Consultation →
Start Your Security Transformation
Tell us a little about your environment using the form below and our security team will reach out to discuss your current posture, your biggest risks, and the managed security approach that fits best.

