

Incident Response Services
Incident Response Services | Threat Detection, Incident Containment, Digital Forensics
Respond to security incidents with a structured approach to detection, containment, investigation, and recovery, supported by experienced cybersecurity professionals.
Fill Out the Form to Connect With Our Response Team
We only use your info to contact you about your incident response needs.
Why Companies Choose AppStudio for Incident Response Services
Battle-Tested Responders
Responders who have run real breaches bring calm playbooks when internal teams are overloaded.
Evidence-First Containment
Forensics preserves evidence while containment stops the bleeding, so legal and recovery options stay open.
A Known Escalation Path
Retainer or on-demand models give you a known escalation path before ransomware or BEC becomes a crisis.
Stronger After Every Incident
Post-incident hardening turns every event into lasting control improvements, not just a closed ticket.
Services
What Our Incident Response Services Cover
Rapid Triage & Containment
- Immediate severity assessment and containment actions to limit blast radius.
- Coordination with IT, leadership, and legal stakeholders under clear roles.
- Playbooks for ransomware, account takeover, data theft, and insider events.
Root-Cause Analysis
- Investigation that identifies initial access, persistence, and impact.
- Timeline reconstruction leadership can use for decisions and disclosure.
- Findings that separate symptoms from the control failures that enabled them.
Memory, Disk & Network Forensics
- Forensic collection and analysis during active and recent breach events.
- Evidence handling suited to internal investigation and external counsel needs.
- Artifact review across endpoints, servers, and network telemetry.
Ransomware & Extortion Response
- Containment and recovery coordination focused on restoring clean operations.
- Support for negotiation and disclosure workflows when counsel directs them.
- Alignment with backup and DR teams for known-good restoration paths.
Compromise Assessment
- Hunt for active or recent unauthorized activity when suspicion is high.
- Scope determination across identities, endpoints, cloud, and email.
- Clear go / no-go guidance on whether a full IR engagement is required.
Post-Incident Hardening
- Control fixes and detection improvements so the same gap cannot be reused.
- Lessons-learned workshops with technical and executive audiences.
- Backlog prioritization tied to residual risk, not generic best practices.
IR Retainer & Readiness
- Retainer options that reserve response capacity and shorten mobilization time.
- Tabletops and runbook reviews before an incident tests your process.
- Integration with MDR and SOC escalation paths.
Reporting & Stakeholder Communication
- Technical and executive reporting suited to boards, insurers, and regulators.
- Status cadence that keeps decision-makers informed without slowing responders.
- Documentation that supports insurance, legal, and customer notification needs.
Solving the Incident Response Challenges that Others Overlook
Business Priorities
Industry Gaps
Our Proven Advantage
Global Standards. Built-In Trust.
We operate with the highest levels of security, privacy, and quality, backed by globally recognized certifications. Our standards are built to meet enterprise and regulatory requirements across industries.
Book a Free Consultation
Pick a time that works for you and walk through your current setup with one of our specialists. You will leave with a clear read on your options and a practical next step, with no obligation.
Rated Among the Top Managed Security Partners
Independent review platforms and analysts consistently rank AppStudio for the things clients care about most: reliability you can plan around, governance you can prove, and operations that scale as you do.


How We Deliver Incident Response & Forensics
Incidents reward preparation and punish hesitation. At AppStudio, response starts with triage and containment, then forensics and hardening so recovery is clean and durable.
IR sits inside our cybersecurity services and MSSP model, with direct escalation from SOC and MDR monitoring.
The outcome is shorter dwell time, clearer answers for leadership, and fewer repeat incidents from the same root cause.
Why Clients Stay With Us
We are measured on containment speed and clarity under pressure. The numbers below are why clients keep IR capacity with us.
Book a Free Consultation →minute target acknowledgment for retainer clients with active critical incidents
times faster average containment versus ad-hoc, unprepared response
of major IR engagements include root-cause and hardening recommendations
What Our Clients Say About Working With Us
Success Stories
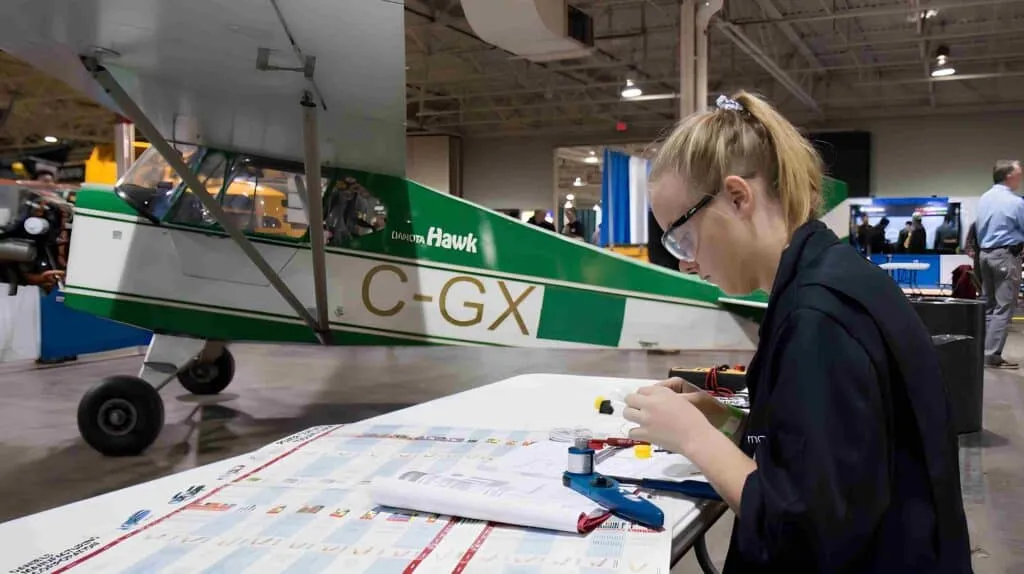
Empowering Future Talent in Trades and Technology
Commissioned by Skills Compétences Canada, we built a national bilingual platform with native apps, a secure CMS, and Canadian cloud infrastructure to promote trades and technology careers at scale.
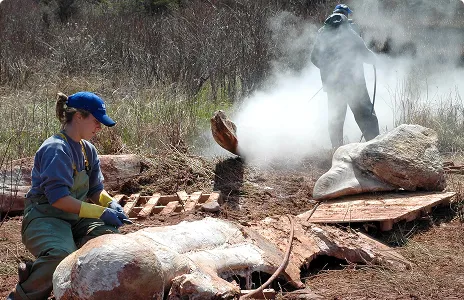
Digitizing Wildlife Surveillance for National Resilience
For the Canadian Wildlife Health Cooperative, we replaced siloed tools with a cloud-native platform that unifies field reports, lab diagnostics, and cross-province analytics in real time.
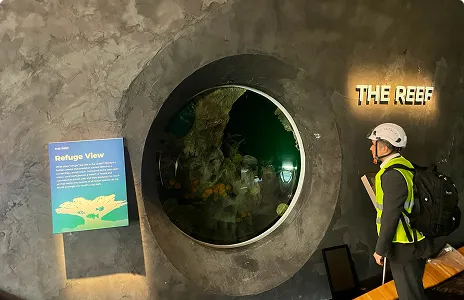
Interactive Learning Through Digital Experience
We unified kiosks, ticketing, and mobile into one cloud-native platform for Seattle Aquarium, raising visitor engagement and streamlining operations across every touchpoint.
Domain-Centric Incident Response for High-Stakes Environments
AppStudio responds to incidents in industries where downtime, regulated data, and customer trust make every hour of dwell time expensive.

Healthcare & Life Sciences
Healthcare & Life Sciences
- Containment that isolates threats without disrupting patient care.
- Forensics and breach scoping aligned to HIPAA notification duties.
- Recovery playbooks that restore EHR and clinical systems first.

Accounting & Financial Services
Accounting & Financial Services
- Rapid containment of wire fraud and account-takeover incidents.
- Forensic timelines built for regulators, insurers, and auditors.
- Recovery that protects trading and settlement windows.

Retail & Consumer Commerce
Retail & Consumer Commerce
- POS and e-commerce breach containment during peak trading.
- Card-skimming and Magecart investigation across storefronts.
- Evidence and scoping mapped to PCI DSS obligations.

Government & Public Sector
Government & Public Sector
- Multi-agency containment with a clear chain of custody.
- Response aligned to CIS, NIST, and public-sector mandates.
- Forensics and reporting that survive oversight and disclosure.

Logistics, Supply Chain & Transportation
Logistics, Supply Chain & Transportation
- Containment that keeps freight moving while the incident is worked.
- Investigation across WMS, TMS, and partner-facing systems.
- Recovery sequencing that prioritizes time-critical operations.

Telecom & Connectivity
Telecom & Connectivity
- Incident containment across core network and subscriber platforms.
- High-volume log correlation to reconstruct intrusion paths.
- SLA-backed mobilization on always-on infrastructure.

Education & eLearning
Education & eLearning
- Ransomware containment that protects exam and term deadlines.
- FERPA-aware breach scoping for student and staff data.
- Account-takeover recovery across campus identity systems.

Travel, Hospitality & Aviation
Travel, Hospitality & Aviation
- Containment across booking, PMS, and POS without downing properties.
- Guest-data breach scoping aligned to PCI and privacy duties.
- Recovery that keeps reservations and check-in running.

High-Tech, SaaS & Software Product Companies
High-Tech, SaaS & Software Product Companies
- Cloud and CI/CD compromise containment across tenants.
- Forensics for secrets exposure, API abuse, and supply-chain intrusions.
- Coordinated customer notification and clean redeployment.

Real Estate & PropTech
Real Estate & PropTech
- Wire-fraud incident response on closing and deposit flows.
- Containment that spans leasing portals and connected building tech.
- Recovery and hardening after business email compromise.

Energy, Oil & Gas
Energy, Oil & Gas
- IT and OT containment that accounts for safety and uptime.
- Response aligned to NERC CIP and IEC 62443 for critical assets.
- Forensics across field, plant, and control-system boundaries.

Manufacturing & Industrial
Manufacturing & Industrial
- Containment that protects production lines and safety systems.
- Investigation of lateral movement between corporate and plant networks.
- Recovery sequencing that restores the floor without reinfection.

Media & Entertainment
Media & Entertainment
- Rapid response to pre-release leaks and asset theft.
- Containment for DDoS and account abuse on live platforms.
- Forensics across content, streaming, and distribution pipelines.

Legal Services & Law Firms
Legal Services & Law Firms
- Privilege-aware containment and confidential breach scoping.
- Business email compromise investigation for partner accounts.
- Post-incident evidence packaged for clients and insurers.

Nonprofit Organizations
Nonprofit Organizations
- Right-sized response for lean teams hit by ransomware or fraud.
- Donor-data breach scoping and clear notification support.
- Recovery and hardening that fit a constrained budget.

Pharmaceuticals & MedTech
Pharmaceuticals & MedTech
- Containment tuned to validated lab and production environments.
- Breach scoping for regulated R&D and patient-trial data.
- Recovery that preserves GxP and 21 CFR Part 11 integrity.
Trusted When the Question Is No Longer If, but How Fast
Every organization will face an incident. The difference is whether responders already know your environment and escalation path.
Combine IR retainers with cybersecurity services or a full MSSP so detection and response are one motion. Continuity support is available through IT managed services.
If you want a team that can contain, investigate, and harden, book a consultation before you need one.
Book a Free Consultation →
Frequently Asked Questions
Contain. Investigate. Harden.
Stand up incident response and digital forensics that stop active threats, answer root cause, and close the gaps attackers used.
Book a Free Consultation →
Request a Consultation
Tell us a little about your setup using the form below and our service delivery team will reach out to talk through your environment, your priorities, and the approach that fits best.

